Understanding Digital Forensics and Its Importance
In a rapidly evolving digital landscape, the importance of digital forensics cannot be overstated. Digital forensics pertains to the process of collecting, analyzing, and preserving digital evidence from various devices, including smartphones, computers, and external storage solutions. As individuals and organizations increasingly rely on digital technology for daily operations, the need for effective methods to retrieve and analyze digital data in legal contexts becomes paramount. When exploring options, read more about the capabilities and services provided by forensic experts to understand how they can assist in your investigations.
What Is Digital Forensics?
Digital forensics is a specialized field that encompasses the recovery and investigation of material found in digital devices. It is utilized in both civil and criminal litigation, focusing on preserving, analyzing, and presenting data in a legally acceptable manner. This field combines aspects of law, computer science, and investigative techniques to uncover evidence that can substantiate claims or establish guilt in various scenarios, including cybercrime, fraud, and divorce proceedings.
Key Applications of Digital Forensics
Digital forensics plays a critical role in numerous applications, including:
- Criminal Investigations: Law enforcement agencies utilize forensic techniques to extract evidence from devices involved in criminal activities.
- Corporate Security: Companies employ digital forensics to investigate breaches of security, employee misconduct, and data theft.
- Legal Proceedings: In the context of litigation, digital evidence can support claims in civil disputes, including divorce cases and intellectual property disputes.
The Role of Digital Forensics in Modern Investigations
As technology permeates every aspect of our lives, the volume of digital evidence available is increasing exponentially. Investigators rely on digital forensics to unveil hidden or deleted information that traditional investigation methods might overlook. This field has become indispensable, providing clarity and evidence that can be crucial for achieving justice.
Types of Digital Evidence Analyzed
Data Recovery from Smartphones
Smartphones are among the most frequently analyzed devices in digital forensics. They often contain vital information such as call logs, text messages, email correspondence, and social media activity. The forensic extraction process involves bypassing security features to retrieve existing and deleted data, enabling investigators to obtain comprehensive insights into user interactions.
Analysis of Computer Systems
Computers hold a wealth of information relevant to various investigations. Digital forensic experts examine hard drives, operating systems, and installed applications to trace user actions and uncover potentially incriminating evidence. This analysis can reveal internet browsing history, file downloads, and software usage, which could be pivotal in a case.
Examination of External Storage Devices
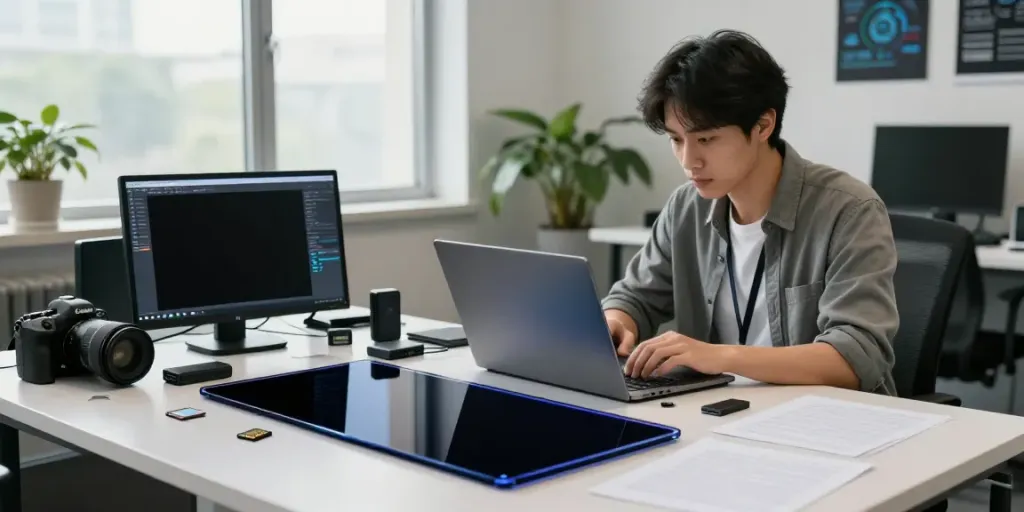
External storage media like USB drives, SD cards, and cloud storage are frequently used to store or transfer sensitive data. Examining these devices involves recovering data that may be deleted or hidden. Forensic analysts employ sophisticated software tools to restore lost files and investigate file structures, access logs, and other indicators of usage.
The Digital Forensics Process
Initial Consultation and Evidence Collection
The digital forensics process often begins with a consultation where the forensic team evaluates the scope of the investigation and identifies the relevant devices. Proper evidence collection is crucial, as it ensures that the data will remain intact for analysis. Investigators must follow strict protocols to maintain the integrity of the evidence, documenting each step in detail.
Analysis Techniques Used in Digital Forensics
After data collection, forensic analysts apply various methods to examine the evidence. Techniques include file carving, email recovery, and analysis of registry data, depending on the investigation's needs. Each method is tailored to the specific device and circumstances, ensuring comprehensive coverage of all potential evidence.
Reporting Findings and Legal Implications
Once the analysis is complete, forensic experts compile their findings into detailed reports that outline the methods used, evidence recovered, and potential implications. These reports are critical, as they serve as formal documentation that can be presented in court or utilized in negotiations. The ability to articulate findings clearly is essential for the credibility and acceptance of digital evidence in legal proceedings.
Challenges and Limitations in Digital Forensics
Technical Barriers to Data Recovery
Digital forensics is not without its challenges. Various technical barriers, such as encryption, data corruption, and the use of advanced security features, can impede the recovery process. Analysts need to stay updated on the latest technological developments to effectively counter these challenges.
Legal and Ethical Considerations
Legal constraints also pose significant challenges in digital forensics. Investigators must operate within the bounds of the law, ensuring they respect privacy rights and obtain necessary permissions before accessing data. Ethical considerations are paramount, as the misuse of digital forensics tools can lead to breaches of trust and legal repercussions.
Common Misconceptions About Digital Forensics
There are many misconceptions surrounding digital forensics. One common belief is that once data is deleted, it is permanently lost. However, with advanced recovery techniques, forensic experts can often retrieve information that users believe to be irretrievable. Another misconception is that any individual with technical skills can perform forensic investigations, but this field requires specialized training and experience to interpret data accurately.
Future Trends in Digital Forensics for 2026
Emerging Technologies Impacting Digital Investigations
As technology evolves, so do the techniques used in digital forensics. The advent of artificial intelligence and machine learning is expected to dramatically impact how data is analyzed, enabling quicker and more accurate assessments of large volumes of data.
The Increasing Need for Digital Forensics in Businesses
With businesses facing rising cyber threats and regulatory requirements, the demand for digital forensics services is growing. Companies are increasingly recognizing the value of having forensic capabilities to protect sensitive data and respond effectively to incidents.
Predictions for Digital Forensics Practices in the Next Decade
In the coming years, digital forensics is likely to become more integrated into routine business practices and criminal investigations. Organizations may implement in-house forensic frameworks and collaborate closely with forensic specialists to ensure robust data security and compliance with legal standards.
What Are the Costs Involved in Digital Forensics?
The costs associated with digital forensics can vary significantly based on the complexity of the case, the type of device, and the volume of data to be analyzed. Factors such as the urgency and specific requirements of the investigation also influence pricing structures. Clients should seek initial consultations to understand potential costs and the scope of services offered.
How Can You Ensure Evidence is Preserved?
Preserving digital evidence is crucial for any investigation. Clients should avoid using the devices in question to prevent data from being overwritten. Proper storage and transfer techniques must be employed to maintain evidence integrity, including the use of write-blocking devices during data extraction.
What Types of Devices Can Be Analyzed?
Digital forensics can apply to a wide array of devices, including smartphones, laptops, desktops, servers, external hard drives, and even IoT devices. Analysts will assess the type of device and its condition to determine the most effective analysis methods.